SaaS and platforms
Can a user get premium without paying? Can one customer see another customer's data? I test the logic behind your product, not only the OWASP checklist. You get findings your developers can reproduce and fix the same week.
Manual web and API testing focused on business logic: payment and billing flows, tenant isolation, access control, race conditions. Fixed price after a 30-minute scoping call. A written report you can hand to your customer, insurer or auditor.
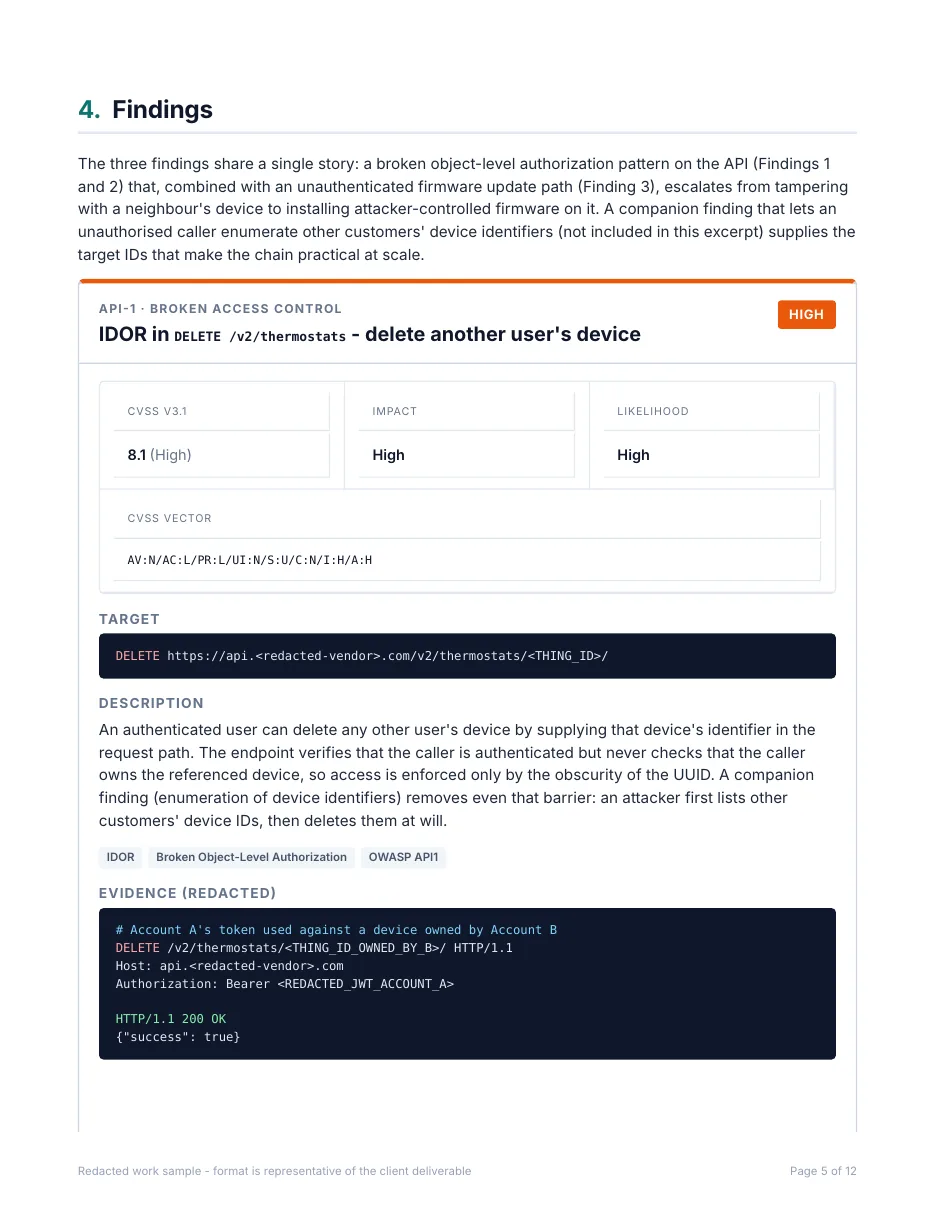
# Account A's token used against a device owned by Account BDELETE /v2/thermostats/<THING_ID_OWNED_BY_B>/ HTTP/1.1Host: api.<redacted-vendor>.comAuthorization: Bearer <REDACTED_JWT_ACCOUNT_A>HTTP/1.1 200 OK{"success": true}Can a user get premium without paying? Can one customer see another customer's data? I test the logic behind your product, not only the OWASP checklist. You get findings your developers can reproduce and fix the same week.
Sell penetration testing to your clients without hiring a tester. I test under your brand, deliver in your report template, and you keep the client relationship. Typical triggers: a cyber insurance questionnaire, a client's customer asking for proof, a new service line in your catalog.
Your client's audit needs a technical test with evidence. I deliver it white-label, scoped to what the auditor asks for, on the audit's timeline.
Pick one client who needs an external test or has an audit this quarter. I’ll run it under your brand at no cost to you.
One pilot per partner. Testing starts after your client signs a testing authorization.
A document your developers can act on and your insurer or auditor can accept. Short and to the point: no filler pages, no pie charts nobody reads.
From $3,000 for a small web application. The exact price is in the written test plan after the scoping call.
What is in scope: application, roles, environments, API, timeline. You get a written test plan, timeline and fixed price within 24 hours.
Manual testing against the plan. Written update every 2-3 days. Critical findings reported the same day, with a workaround if one exists.
The report plus a call to go through the findings with your developers. For white-label engagements, with your client's team under your brand.
After fixes, within 90 days of the report, I re-verify every finding and issue the updated report.
The person on the scoping call is the person who tests and writes your report. No account managers, no handoff to juniors.
I am Alex Konoriev, a penetration tester and security engineer based in Kyiv. Before testing I built security infrastructure at Samsung and on Ericsson projects, which is why my reports read like something a development team can act on.
Scope and testing windows are agreed in writing before I start. I prefer a staging environment; on production I avoid destructive tests unless you sign off on them explicitly, keep request rates low, and never extract data beyond what is needed as proof.
No. Black-box testing works without it. Source code review is available as an add-on and usually finds more in less time.
A typical SaaS application with login, a few user roles and an API: 40 to 60 hours of testing. I confirm the hours and the timeline after the scoping call.
From $3,000 for a small web application. Larger scopes get a fixed price in the written test plan after the scoping call.
You still receive the full report of what was tested and held up. For an insurer or auditor that is the document they need.
NDA with you, report in your template and brand, no contact with your client unless you want me on the call. You set the price to your client. I don’t sell managed services or remediation, and a non-solicit clause goes into our agreement.
I do the technical testing and the evidence. I work alongside your GRC consultant or auditor rather than replacing them.
Book a scoping call. You leave with a written test plan and a fixed price, whether or not you go ahead.